Home / Trending Programs 2026 / AI-Powered Cybersecurity
Enterprise Cyber Defense • 2026 Specialization

AI-Powered Cybersecurity Course

Architect Autonomous SOC Operations, SIEM Threat Hunting & Zero Trust Cloud Defense

Master both offensive adversarial penetration testing and AI-augmented blue team defense. Learn modern ethical hacking, OWASP Top 10 exploitation, network penetration testing, Splunk/Wazuh SIEM threat hunting, automated incident response, and AI-driven behavioral anomaly detection.
7 Months Duration
320+ Hrs Live Mentor Labs
1-on-1 Mentor Guidance
Virtual Range Isolated Cyber Lab
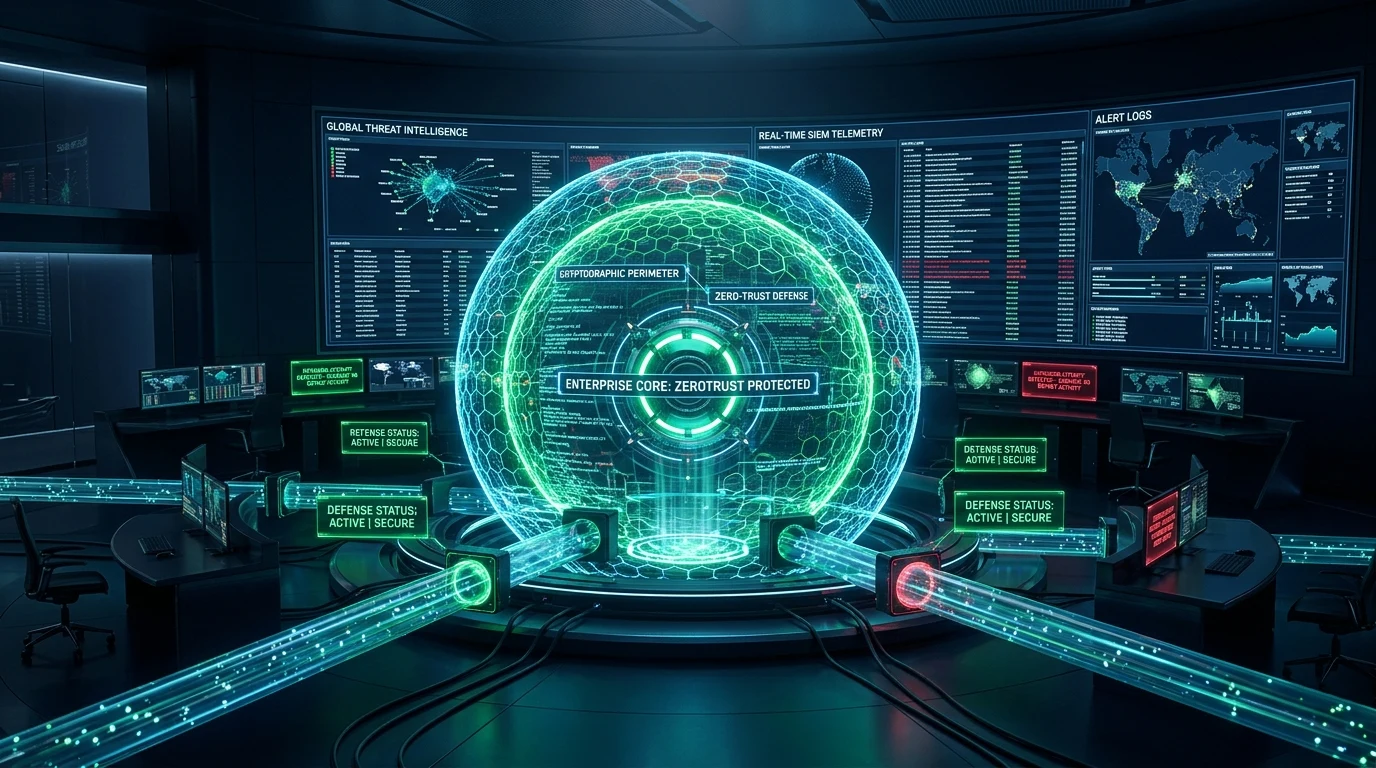
AI-Powered Cybersecurity 3D Cyber Range Visual
Upcoming 2026 Batch Admissions
Limited 25 Seats • Weekend & Evening Batches

Get Expert Course Guidance

Speak with a Principal Architect & get a customized roadmap, syllabus, and 0% EMI plans.

+91
100% Confidential 15-Min Fast Callback 1-on-1 Career Mentorship
🎓
Dual Certification Industry Recognized Certification
💻
Virtual Cyber Range Isolated Offensive & SOC Defense Lab
👥
1:1 Technical Mentorship Architecture Reviews by Lead Engineers
💼
1-on-1 Career Mentorship Dedicated Interview Prep & Hiring Partner Drives
ENTERPRISE THREAT REALITIES

Beyond Theory: Real Attacks in Live Cyber Ranges

Reading textbooks cannot prepare you for live ransomware or sophisticated nation-state intrusions. 4Achievers trains you inside isolated live cyber ranges simulating real adversary tactics and automated SIEM defenses.

01

Offensive Red Team Penetration Testing

Think like a malicious actor. Exploit web applications using Burp Suite Pro, bypass firewalls, escalate privileges in Linux/Windows domains, and execute stealthy network pivoting.

02

Enterprise SIEM, Splunk & Wazuh EDR

Ingest millions of security events per second into Splunk. Write advanced SPL threat hunting queries, configure Wazuh endpoint agents, map indicators to MITRE ATT&CK, and dissect memory dumps.

03

AI Threat Hunting & Cloud Zero Trust

Deploy machine learning models to detect unknown zero-day anomalies. Architect multi-account AWS cloud defense with GuardDuty, automated SOAR remediation playbooks, and strict Zero Trust principles.

COMPREHENSIVE SYLLABUS

Industry-Aligned Practical Modules

A step-by-step technical progression designed by veteran CISOs. Progress from defensive networking and ethical hacking to enterprise SIEM threat hunting, cloud security, and AI defense automation.

MODULE 01 • 7 WEEKS

Networking Protocols, Linux Security & Defensive Foundations

Establish deep network packet inspection capabilities, Linux systems hardening, and applied cryptography.

MODULE 1.1
TCP/IP Protocol Suite & Wireshark Analysis
Three-way handshakes, ARP spoofing detection, DNS exfiltration analysis, and deep packet inspection with Wireshark.
MODULE 1.2
Linux Kernel Hardening & File Integrity
Sudoers auditing, SSH key governance, kernel sysctl security tuning, iptables/UFW firewalls, and AIDE file integrity monitoring.
MODULE 1.3
Applied Cryptography & Public Key Infrastructure
Symmetric vs asymmetric ciphers (AES-256, RSA, ECC), TLS 1.3 certificate chains, OpenSSL commands, and hashing algorithms.
MODULE 1.4
Identity Governance, Active Directory & Kerberos
Windows Active Directory architecture, Domain Controllers, Kerberos authentication tickets, LDAP, and password policies.
HANDS-ON LIVE PROJECT: Enterprise Network Perimeter Hardening with Subnet Micro-Segmentation, Firewalls, and Automated Packet Anomaly Detection.
MODULE 02 • 7 WEEKS

Offensive Security, Web Exploitation & Penetration Testing

Learn adversarial tactics, discover critical OWASP Top 10 vulnerabilities, and conduct professional penetration tests.

MODULE 2.1
Reconnaissance, Footprinting & Nmap Scanning
Passive OSINT gathering, DNS enumeration, active port scanning with Nmap NSE scripts, and service banner grabbing.
MODULE 2.2
OWASP Top 10 Web Exploitation with Burp Suite
SQL Injection (SQLi), Server-Side Request Forgery (SSRF), Broken Object Level Authorization (BOLA/IDOR), and XSS.
MODULE 2.3
Privilege Escalation & Lateral Movement
Linux SUID binaries, cron jobs, sudo rights abuse; Windows token impersonation, Pass-the-Hash, and Mimikatz tradecraft.
MODULE 2.4
Metasploit Framework & Vulnerability Reporting
Exploit modules, meterpreter payloads, staging, evasion tactics, and compiling executive CVSS v3.1 audit reports.
HANDS-ON LIVE PROJECT: Full-Scope Web Application & Network Penetration Audit with Proof-of-Concept Exploits, CVSS Scoring, and Executive Report.
MODULE 03 • 7 WEEKS

SIEM Threat Hunting, Splunk & SOC Incident Response

Deploy enterprise SIEM platforms, ingest live endpoint telemetry, track adversaries using MITRE ATT&CK, and handle incidents.

MODULE 3.1
Splunk Enterprise Architecture & SPL Queries
Indexers, forwarders, search heads, writing complex Search Processing Language (SPL) queries, eval, stats, and alert thresholds.
MODULE 3.2
Endpoint Detection & Response (EDR) with Wazuh
Deploying Wazuh agents across endpoints, Sysmon log collection, rootkit detection, and real-time behavioral alerts.
MODULE 3.3
MITRE ATT&CK Mapping & Threat Intelligence
Tactics, Techniques, and Procedures (TTPs), IoC ingestion (STIX/TAXII), AlienVault OTX feeds, and correlation rules.
MODULE 3.4
Digital Forensics & Incident Handling (DFIR)
Memory acquisition with FTK Imager, volatile RAM inspection with Volatility 3, timeline reconstruction, and containment.
HANDS-ON LIVE PROJECT: 24/7 Enterprise SOC Simulation: Investigating an Active APT Intrusion, Tracking IoCs in Splunk, and Incident Containment.
MODULE 04 • 7 WEEKS

AI Threat Automation, Cloud Security & Zero Trust Architecture

Harness machine learning models for anomaly detection, secure AWS cloud environments, and automate SOAR response playbooks.

MODULE 4.1
AI-Driven Threat Hunting & Behavioral Anomaly Models
Isolation Forests, autoencoders for network telemetry, detecting beaconing malware, and automated triage scoring.
MODULE 4.2
Cloud Security Posture (AWS GuardDuty & IAM)
VPC flow log monitoring in Athena, GuardDuty machine learning threat findings, AWS Security Hub, and SCP controls.
MODULE 4.3
SOAR Playbook Automation & Instant Quarantine
Building automated playbooks with Shuffle/Cortex to block malicious IPs, revoke compromised API keys, and isolate hosts.
MODULE 4.4
Zero Trust Architecture & Enterprise Governance
NIST SP 800-207 Zero Trust guidelines, micro-segmentation, continuous posture verification, and SOC 2 / ISO 27001 readiness.
HANDS-ON LIVE PROJECT: Autonomous AI SOC Agent System on AWS: Detecting Zero-Day Attacks and Executing Automated Quarantine SOAR Playbooks.
CYBER RANGE PORTFOLIO

Industry Cybersecurity Live Projects

Execute real-world threat emulation and SOC investigations inside isolated cloud cyber ranges. Prove hands-on security competence to enterprise hiring committees.

LIVE PROJECT 01 • SOC & AI AUTOMATION

Automated SOC Incident Triage & Quarantine System

A blue team defensive platform integrating Splunk SIEM and Wazuh EDR with machine learning anomaly scoring to detect and quarantine infected hosts in real time.

SIEM CORE: Splunk Enterprise with custom SPL hunting queries
ENDPOINT AGENTS: Wazuh EDR + Windows Sysmon event ingestion
AI DETECTION: Scikit-learn Isolation Forest behavioral anomaly model
SOAR ACTION: Automated firewall host isolation + Slack alert dispatch
LIVE PROJECT 02 • CLOUD ZERO TRUST

Cloud-Native Zero Trust Defense Architecture on AWS

An enterprise AWS cloud defense infrastructure featuring multi-account segregation, continuous IAM least privilege enforcement, and automated GuardDuty response.

CLOUD DEFENSE: AWS GuardDuty + AWS Security Hub + Athena analytics
TELEMETRY INGEST: VPC Flow Logs + CloudTrail centralized S3 bucket
POLICY ENFORCEMENT: Service Control Policies (SCPs) + AWS KMS encryption
ZERO TRUST AUDIT: Prowler CIS AWS Benchmark compliance score of 98.4%
LIVE PROJECT 03 • FORENSICS & ATT&CK

Enterprise Ransomware Emulation & Forensic Audit

A comprehensive threat emulation scenario executing benign ransomware payloads in an isolated sandbox, analyzing memory artifacts, and documenting the MITRE ATT&CK kill chain.

THREAT EMULATION: Atomic Red Team + Custom Python Encryptor in sandbox
MEMORY FORENSICS: Volatility 3 process injection and DLL dump analysis
FRAMEWORK MAPPING: Mapped to 14 MITRE ATT&CK Enterprise techniques
PROJECT OUTCOME: CISO Executive Briefing + Sigma detection rules
SECURITY TOOLCHAIN

Master the Modern Cybersecurity Stack

Learn the exact industry-standard defensive and offensive security tools required by modern security operation centers and pen testing consultancies.

SIEM
Splunk Enterprise
Security information & event management, SPL queries, and alerting
PACKET ANALYSIS
Wireshark
Deep packet inspection, protocol dissection, and network stream carving
WEB SECURITY
Burp Suite Pro
Web vulnerability proxy, repeater, intruder, and OWASP testing
PEN TESTING
Metasploit
Exploit automation, payload generation, and lateral movement
NETWORK SCAN
Nmap
Network exploration, port discovery, and vulnerability NSE scripts
EDR DEFENSE
Wazuh EDR
Open-source endpoint detection, rootkit checks, and active response
CLOUD SECURITY
AWS GuardDuty
Intelligent threat detection and continuous security monitoring
IDS / IPS
Snort & Suricata
Network intrusion detection rules and real-time packet filtering
FORENSICS
Volatility 3
Advanced memory volatile forensics and malware artifact discovery
AUTOMATION
Python Security
Custom socket programming, exploit scripts, and log parsers
SECURITY OS
Kali Linux
Comprehensive penetration testing and digital forensics platform
THREAT INTEL
MITRE ATT&CK
Adversary behavioral classification and detection coverage matrix
ADMISSIONS • 2026 SPECIALIZATION

Apply for AI-Powered Cybersecurity

Submit your details to receive the comprehensive 28-week curriculum breakdown, cloud cyber range lab details, and connect with our senior career counsellors.

🔒 Verified Data Privacy: Your details are encrypted and used strictly for senior career counsellorsling. Zero spam guaranteed.
COMMON QUESTIONS

Frequently Asked Questions

Direct answers regarding red vs blue team coverage, cyber range lab environments, certifications, and career placement.

Do I need prior coding or cybersecurity experience to enroll?+
No prior cybersecurity background is needed. Basic computer hardware and networking knowledge is helpful. We build up from TCP/IP, Linux commands, and network protocols to advanced ethical hacking and defense.
What are the batch timings and training options?+
We offer classroom batches in Noida Sector 62 / Sector 16 and live instructor-led online training across India. Weekend batches for working IT professionals and Weekday batches for graduates are available.
How are the hands-on cyber range labs conducted?+
All hands-on offensive penetration testing and SOC defensive simulations run inside isolated, cloud-hosted virtual labs. You access Kali Linux, vulnerable target machines (OWASP Juice Shop, DVWA), Splunk SIEM, and Wazuh EDR safely.
Does this program prepare me for global cybersecurity certifications?+
Yes. The curriculum directly maps to the domains of CompTIA Security+, CEH (Certified Ethical Hacker), and AWS Certified Security - Specialty, equipping you with practical skills to clear these examinations.
What 1-on-1 Career Mentorshipand interview preparation is provided?+
Our Career Mentorship Team conducts technical mock interviews covering SOC incident response scenarios, log analysis, threat intelligence, penetration testing reports, and connects you directly with 350+ corporate hiring partners across India.
What job roles can I target after graduating?+
Graduates target high-demand roles including SOC Analyst (L1/L2), Cyber Threat Intelligence Analyst, Penetration Tester / VAPT Specialist, Cloud Security Associate, and Information Security Analyst.

📊 Cyber Security, Ethical Hacking (CEH v13), VAPT & SOC Analyst in India (Noida, Delhi NCR, Bangalore, Mumbai, Pune, Hyderabad & Online) — 2026 Fees, Batch Schedule, Syllabus & Placement Report

Compare 4Achievers' updated 2026 fee structure, 0% No-Cost EMI plans, upcoming weekday/weekend cohorts, hands-on module breakdown, and top hiring companies across Noida Sector 62, Bangalore Whitefield/ORR, Hyderabad HITEC City, Pune Hinjewadi, Mumbai BKC & Gurgaon Cyber City.

1. 2026 Course Fee Structure, Duration & 0% EMI Options in India (Noida, Delhi NCR, Bangalore, Mumbai, Pune, Hyderabad & Online)

Training TrackDuration2026 Course Fee0% No-Cost EMILab & Placement Support
Self-Paced + Cloud SandboxFlexible (1 Yr Access)₹19,500AvailableRecorded Labs + Resume Review
Live Instructor-Led (Pan-India Live Online & Campus Hybrid) ⭐ Most Popular4 Months (160+ Hours Live Cyber Range & VAPT Labs)₹29,500₹3,208 / month (0% EMI)24/7 Live Sandbox + Unlimited Mock Interviews
100% Placement-Assisted Job Bootcamp4 Months (160+ Hours Live Cyber Range & VAPT Labs) + Internship₹38,500Up to 12 Months 0% EMIDedicated Placement Cell + 6-Week Industrial Letter

2. Upcoming November 2026 Batch Schedule (India (Noida, Delhi NCR, Bangalore, Mumbai, Pune, Hyderabad & Online))

Batch TypeStart DateClass Timings (IST)ModeSeat Availability
Weekday Regular Cohort06 Nov 2026 (Mon–Fri)10:00 AM – 12:00 PMClassroom & Live Online🔥 Only 4 Seats Left
Weekend Working-Pro Cohort08 Nov 2026 (Sat–Sun)11:00 AM – 02:00 PMClassroom & Live Online✅ Open (5 Seats Left)
Evening Fast-Track Cohort11 Nov 2026 (Mon–Fri)08:00 PM – 10:00 PMLive Interactive Online✅ Open for Enrollment

3. 2026 Updated Syllabus Modules & Tool Stack (Kali Linux, Burp Suite Pro, Nmap, Metasploit, Wireshark, Nessus, Splunk SIEM, IBM QRadar, CrowdStrike EDR, OWASP ZAP & AWS Cloud Security)

ModuleCore Topics, Practical Labs & Deliverables
Module 1Networking Security, TCP/IP Packet Analysis, Linux Hardening & Cryptography Essentials
Module 2Ethical Hacking (CEH v13): Reconnaissance, Vulnerability Scanning, System Hacking & Malware
Module 3Web Application & API VAPT: OWASP Top 10, SQLi, XSS, SSRF, IDOR & Burp Suite Exploitation
Module 4SOC Analyst L1/L2 Operations: Splunk SPL Queries, QRadar SIEM Log Correlation & Incident Response
Module 5Cloud Security (AWS/Azure IAM, WAF, GuardDuty), Active Directory Attacks & Digital Forensics
Module 6Live Bug Bounty & Red-Team/Blue-Team Cyber Range Capstone + CEH/CompTIA Security+ Prep

4. Top Hiring Companies & 2026 Salary Packages in India (Noida, Delhi NCR, Bangalore, Mumbai, Pune, Hyderabad & Online)

Local Tech CorridorsTop Hiring MNCs & GCCsFresher (0–2 Yrs)Mid-Level (2–5 Yrs)Senior / Lead (5+ Yrs)
Noida Sector 62, Bangalore Whitefield/ORR, Hyderabad HITEC City, Pune Hinjewadi, Mumbai BKC & Gurgaon Cyber CityTCS, Infosys, HCLTech, Accenture, Deloitte USI, Walmart Global Tech, JPMorgan, Barclays & Jio Platforms₹6.0 LPA – ₹10.5 LPA₹12.0 LPA – ₹22.0 LPA₹24.0 LPA – ₹45.0 LPA

🎓 Download 2026 Cyber Security, Ethical Hacking (CEH v13), VAPT & SOC Analyst Syllabus PDF, Fee Brochure & Book Free Demo Class

Enter your WhatsApp number below to receive the complete module-wise PDF, scholarship discount coupon, and free demo link for India (Noida, Delhi NCR, Bangalore, Mumbai, Pune, Hyderabad & Online):

📌 Page Quick Jump: 1. Overview & Highlights 2. 2026 Curriculum & Labs 3. Fee Structure & ROI 4. Career Mentorship & FAQs
Explore Official Noida Campus & Live Batches →
📊 AI Powered Cybersecurity (Noida, Delhi NCR, Mumbai, Bangalore & Online) — 2026 Updated Batch, Fee & Lab Overview
Training Track (2026) Duration & Mode Hands-On Cloud / ERP Labs Fee & Scholarship Options Career Mentorship
Fast-Track Certification 8–10 Weeks (Weekday / Weekend) 24/7 Cloud Sandbox + 2 Live Projects 0% Interest Monthly EMI Available 1-on-1 Resume & Mock Interviews
Executive Master Program 14–20 Weeks (Classroom & Live Online) 24/7 Enterprise Lab + 4 Capstone Projects Up to 50% Merit Scholarship + 0% EMI 1-on-1 Architect Mentorship & Portfolio
🚀 Explore Related 2026 Career Programs, City Training Hubs & Interview Resources
Flagship Cloud & ERP Courses
Top Courses in Noida
2026 Certification Cost & Papers
Trending Skill & Career Tracks
View All 6,400+ Programs Directory →